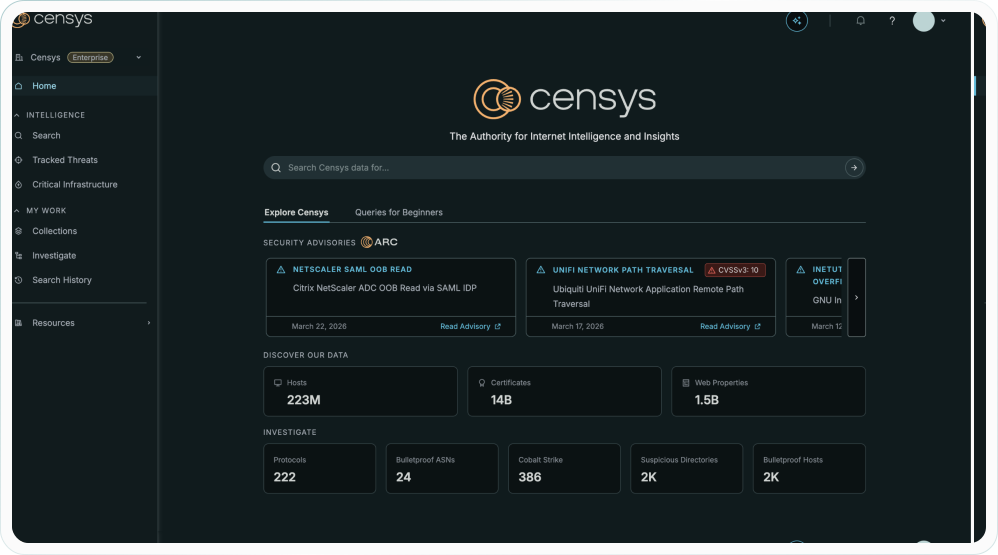
Adversary Investigation is an enterprise add-on module for Censys Core, available to enterprise customers on request. It provides threat hunters, CTI analysts and detection engineers with full access to Censys threat data, enabling search and pivot across attacker infrastructure. The module supports structured, proactive hunting campaigns that move security operations beyond reactive alert triage, covering threat actor infrastructure mapping, detection engineering, and AI-assisted investigation.
Adversary Investigation requires an active Censys Core subscription and adds its capabilities directly on top of the Core platform. It covers four capability themes: search and pivoting with CensEye to automatically surface related infrastructure; forensic attribution with TLS fingerprints, certificate history, and open directory data; workflow tools including Tracked Threats, Investigation Manager, and Live Discovery for ongoing monitoring; and AI Investigations plus a dedicated MCP server for automation and AI-assisted analysis.
Search and Pivoting
Full threat data search lets analysts query and pivot across attacker infrastructure — IPs, certificates, banners and TLS fingerprints. CensEye automates the pivoting process, surfacing related hosts that share observable characteristics with a known indicator, so analysts can rapidly map the full extent of a threat actor's internet presence.
Infrastructure Attribution
JARM, JA4X and JA3S TLS fingerprints identify attacker infrastructure by its TLS behaviour. A certificate history timeline traces SSL patterns used by threat actors over time. Open directory data surfaces file listings on attacker-controlled servers, and Live Discovery performs a real-time scan to confirm what a host is serving right now.
Threat Tracking and Workflow
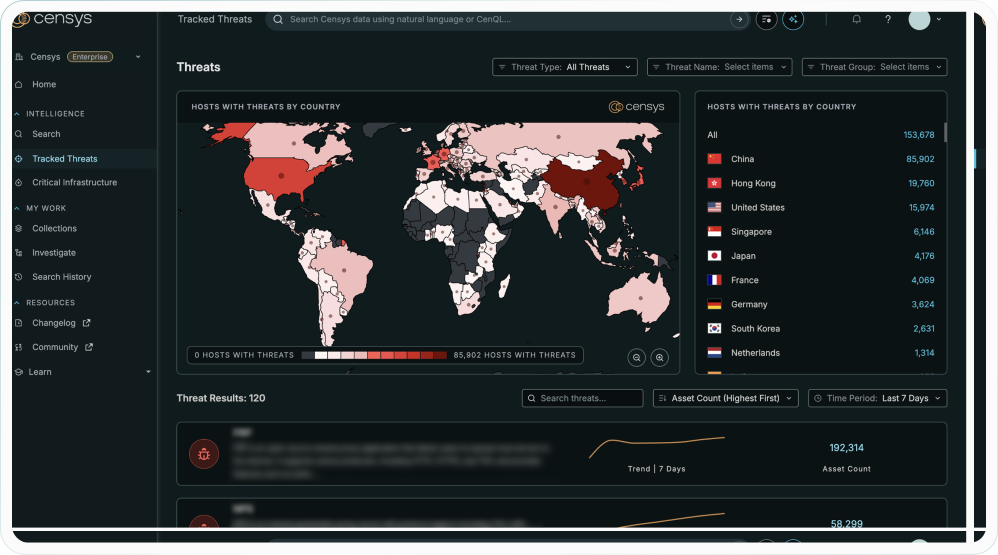
Tracked Threats monitors known threat actor activity continuously, removing the need to re-run hunts manually. Investigation Manager keeps hunting workflows organised and shareable across a team, enabling the structured, proactive campaigns that underpin SOC modernisation. Both tools support the detection engineering workflow, turning hunt findings into durable detection rules.
AI and Automation
AI Investigations supports hypothesis-driven analysis, letting analysts generate and test queries against the Censys Internet Map to accelerate the path from initial indicator to confirmed infrastructure cluster. A dedicated MCP server connects Adversary Investigation with existing security tooling, enabling AI-assisted workflows without leaving the team's current operational environment.
Technical Specifications
Full specifications for Adversary Investigation
Detailed specifications are coming soon — see the datasheet in the Documentation tab for full details in the meantime.
Documentation
Download product documentation and resources
Product Datasheet
A datasheet for this product is available on request. Contact the ExposureGuard team.