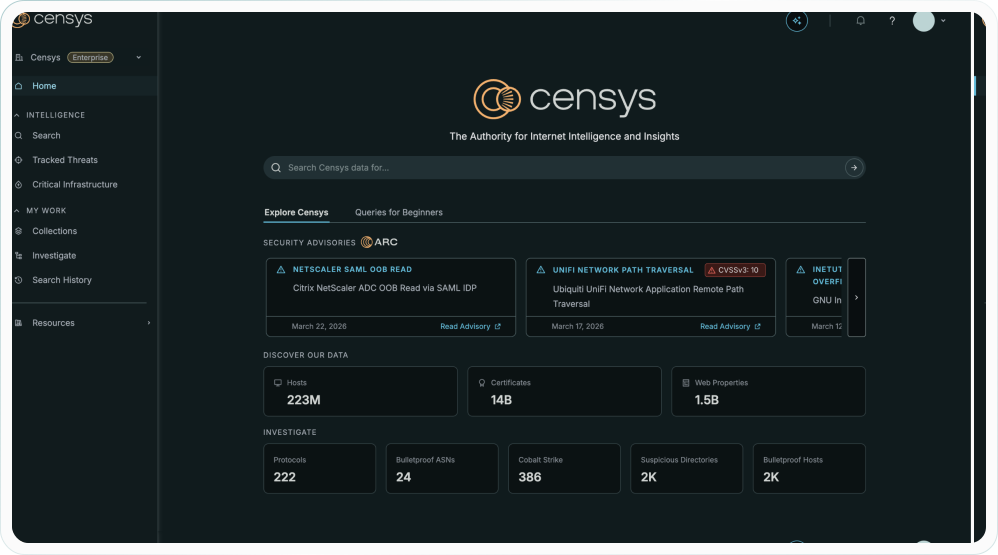
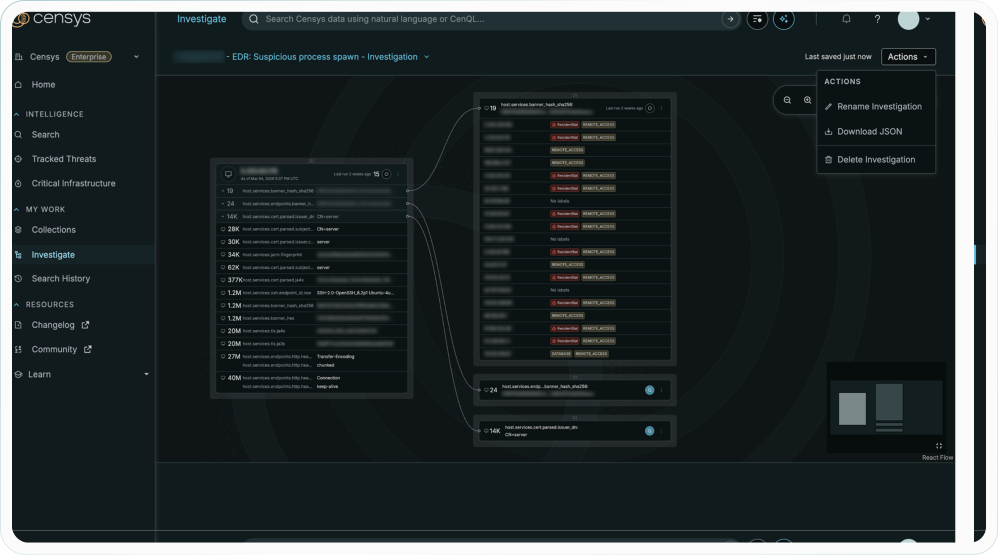
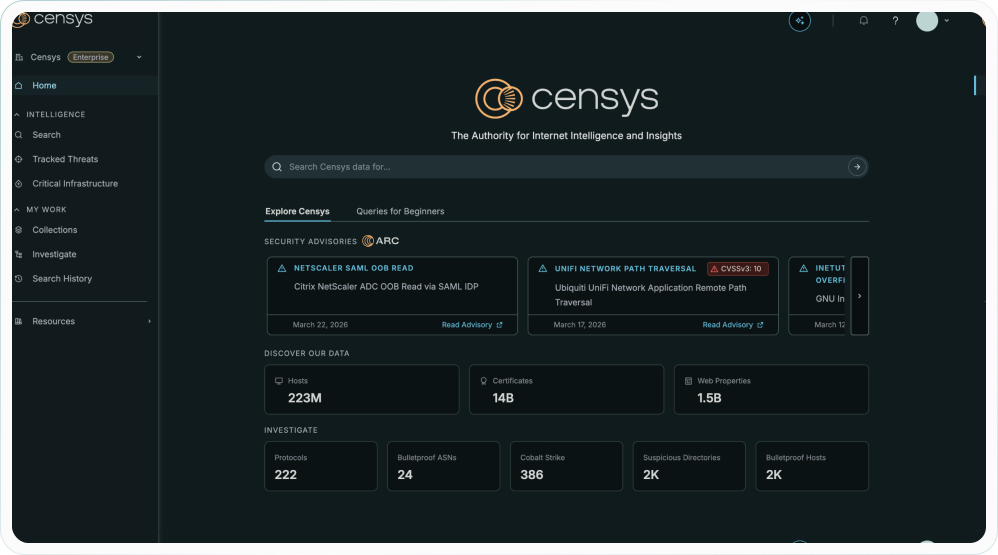
Censys Core is an enterprise subscription, available on request, that includes every Censys Search capability and adds risk data and enriched asset context on top. CVE and Known Exploited Vulnerability risk data is applied directly to internet-facing hosts and web properties, giving security teams a risk-based view of their external footprint without requiring a separate vulnerability scanner. Core also provides the Host Enrichment API for programmatic access to deeper asset context across automated workflows.
Fifteen or more Collections support persistent, structured tracking of asset groups, and Connections allow Censys data to flow directly into SIEM, ticketing, and vulnerability management platforms. Core supports risk-based vulnerability prioritisation, threat detection through host reputation, threat hunting with enriched host data, and SOC alert enrichment. It is also the required platform subscription for the Adversary Investigation and Critical Infrastructure Monitoring add-on modules.
Risk and Vulnerability Context
CVE risk data and Known Exploited Vulnerability flags are applied to each internet-facing host and web property in the Censys dataset. Security teams can prioritise vulnerabilities by exposure risk rather than raw CVSS score, focusing remediation effort on the assets and vulnerabilities that pose the greatest actual threat to the organisation.
Full-Spectrum Search
Core inherits all Censys Search capabilities: nearly the full protocol dataset, CPE software version and lifecycle context, certificate coverage, 31 or more days of host history, and regex query support. SSO via SAML and multi-user organisation access with up to 25 concurrent actions are included for enterprise team management.
Collections and Tracking
Fifteen or more named Collections allow teams to define and persistently track specific sets of assets — IP ranges, domains, ASNs, or complex query-based groupings. Webhooks and Connections push change notifications and asset data downstream automatically, enabling near-real-time monitoring without manual re-query of the Internet Map.
API and Integration
The Host Enrichment API delivers deeper asset context for programmatic workflows. Connections push Censys data into SIEM, ticketing, and vulnerability management platforms. Ten or more output destinations support custom export pipelines. Core is the required subscription for Adversary Investigation and Critical Infrastructure Monitoring add-ons.
Technical Specifications
Full specifications for Censys Core
Detailed specifications are coming soon — see the datasheet in the Documentation tab for full details in the meantime.
Documentation
Download product documentation and resources
Product Datasheet
A datasheet for this product is available on request. Contact the ExposureGuard team.