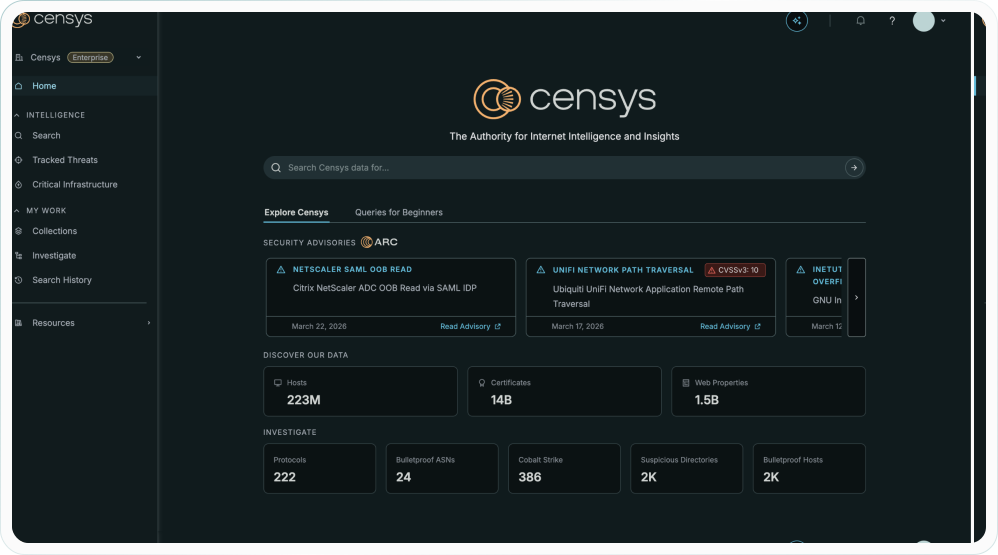
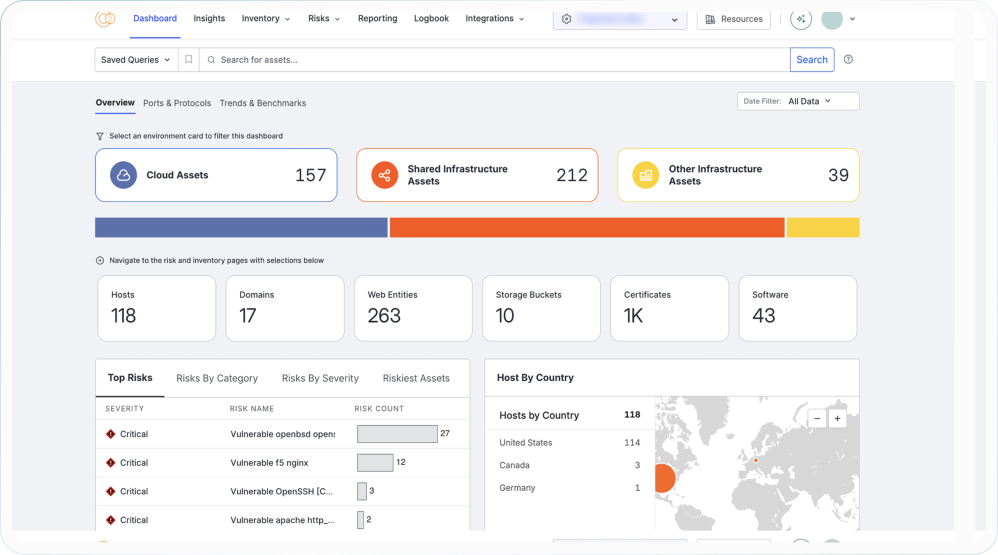
Censys Attack Surface Management is an enterprise subscription that provides continuous, automated discovery and monitoring of an organisation's external attack surface. It inventories internet-facing assets — IP ranges, domains, web properties, and cloud resources — across registered and unregistered infrastructure, then identifies CVE risk and dangling-DNS exposures as they appear. Cloud connectors for AWS, GCP, and Azure correlate cloud asset data with the Censys Internet Map to provide a unified view of hybrid and multi-cloud exposure.
ASM surfaces risk through dashboards, exposure benchmarks, and management reports designed for both security operations and executive audiences. It integrates broadly with the security stack — ticketing systems, SIEM platforms, and vulnerability management tools including Qualys, Tenable, and ServiceNow — to route exposure findings into existing remediation workflows. ASM is suited to enterprise organisations that need ongoing, automated visibility into their external footprint without manual asset enumeration or periodic point-in-time scanning.
Continuous Asset Discovery
ASM continuously enumerates internet-facing assets across all of an organisation's registered infrastructure — IP ranges, domains, acquired brands, subsidiaries, and cloud environments. Discovery is automated and ongoing, so newly provisioned assets, shadow IT, and misconfigured cloud resources appear in the inventory without manual effort from the security team.
Cloud Connector Integration
Native connectors for AWS, GCP, and Azure pull cloud asset inventory directly from each provider and correlate it with the Censys Internet Map. This provides a unified view of which cloud assets are internet-accessible and what they are exposing, closing the gap between cloud infrastructure data and external internet visibility that point-in-time scanning leaves open.
Dashboards and Reporting
Dashboards and exposure benchmarks make the organisation's external attack surface posture visible and comparable over time. Executive-ready management reports summarise exposure trends without requiring technical interpretation, supporting internal governance and third-party audit requirements. Benchmark data helps teams contextualise their posture relative to industry peers.
SIEM and Ticketing Integration
ASM integrates with ticketing systems, SIEM platforms, and vulnerability management tools — including Qualys, Tenable, and ServiceNow — to route exposure findings into existing remediation workflows. This removes the need to manually triage ASM output and ensures exposure findings trigger the same response processes as internally-sourced vulnerability data.
Technical Specifications
Full specifications for Attack Surface Management
Detailed specifications are coming soon — see the datasheet in the Documentation tab for full details in the meantime.
Documentation
Download product documentation and resources