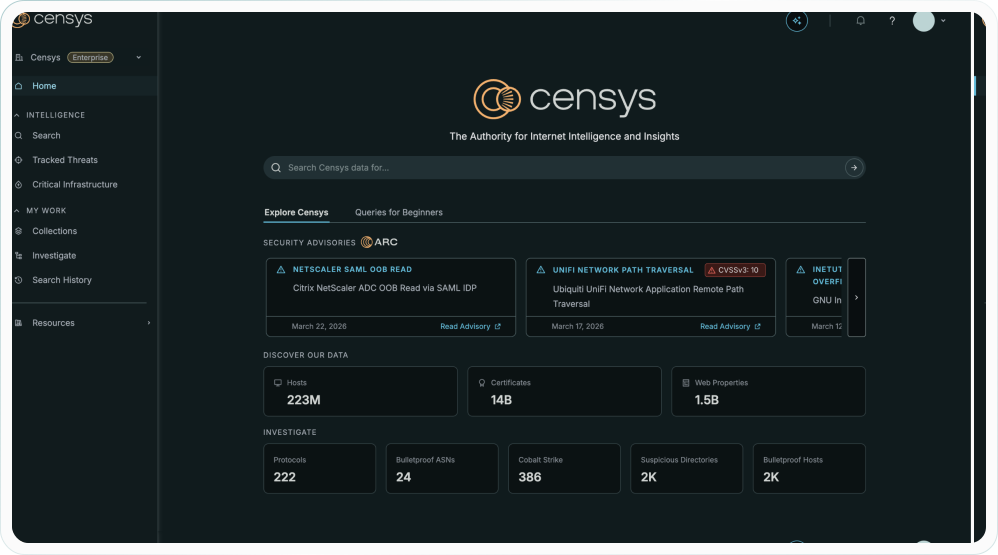
Most tools miss what's genuinely reachable from the internet. Censys scans the full internet across all 65,000 ports to surface exactly what attackers, customers, and regulators can see.
First-party scanning uncovers Internet-exposed assets that internal tools overlook — services on non-standard ports, hosts with self-signed certificates, and assets in residential networks — so your inventory maps what attackers can actually reach.
When Censys ARC identifies a new critical exposure or active exploitation event, confirm reachability in seconds, find every affected internet-facing asset, and launch targeted remediation directly through your existing workflows.
Monitor your attack surface continuously, alerting on meaningful changes — new hosts, ports, certificates, or services — so a new exposure becomes a remediation ticket within the hour rather than a quarterly surprise. Includes EPSS and KEV vulnerability risk scoring.
Integrate with ticketing, vulnerability management, and security tooling to automatically create, route, and close remediation tasks — embedding ASM findings into day-to-day operations rather than leaving them in a separate dashboard.
Generate executive-ready and audit-friendly reports mapping exposure trends and remediation progress — giving leadership evidence-based risk reduction stories, not anecdotes.
When ASM surfaces a risky exposure, pivot directly into the Censys Platform to investigate adversary context — tracking reused certificates and domains and turning asset remediation findings into SOC-ready intelligence.
Censys scans all 65,000 ports globally with first-party scanners, uncovering internet-exposed assets that internal tools miss — including services on non-standard ports, hosts in residential IP ranges, and assets with self-signed certificates that bypass conventional scanners.
Continuous surface monitoring alerts on meaningful changes to your attack surface — new hosts, open ports, certificate reissues, or changed services — enriched with EPSS and KEV risk scoring so new exposures surface for remediation within hours, not quarterly reviews.
When a critical CVE or active exploitation event is flagged, Censys ARC confirms asset reachability in seconds and identifies every internet-facing asset in scope — enabling immediate targeted response before attackers can act on the exposure.
Native integrations with ticketing, vulnerability management, and SIEM platforms automatically create and route remediation tasks, embedding ASM findings into existing day-to-day operations rather than leaving them isolated in a separate dashboard.
We're an authorised Censys reseller. Call us on (02) 9388 1741 or send us your requirements and we'll recommend the right product and tier.